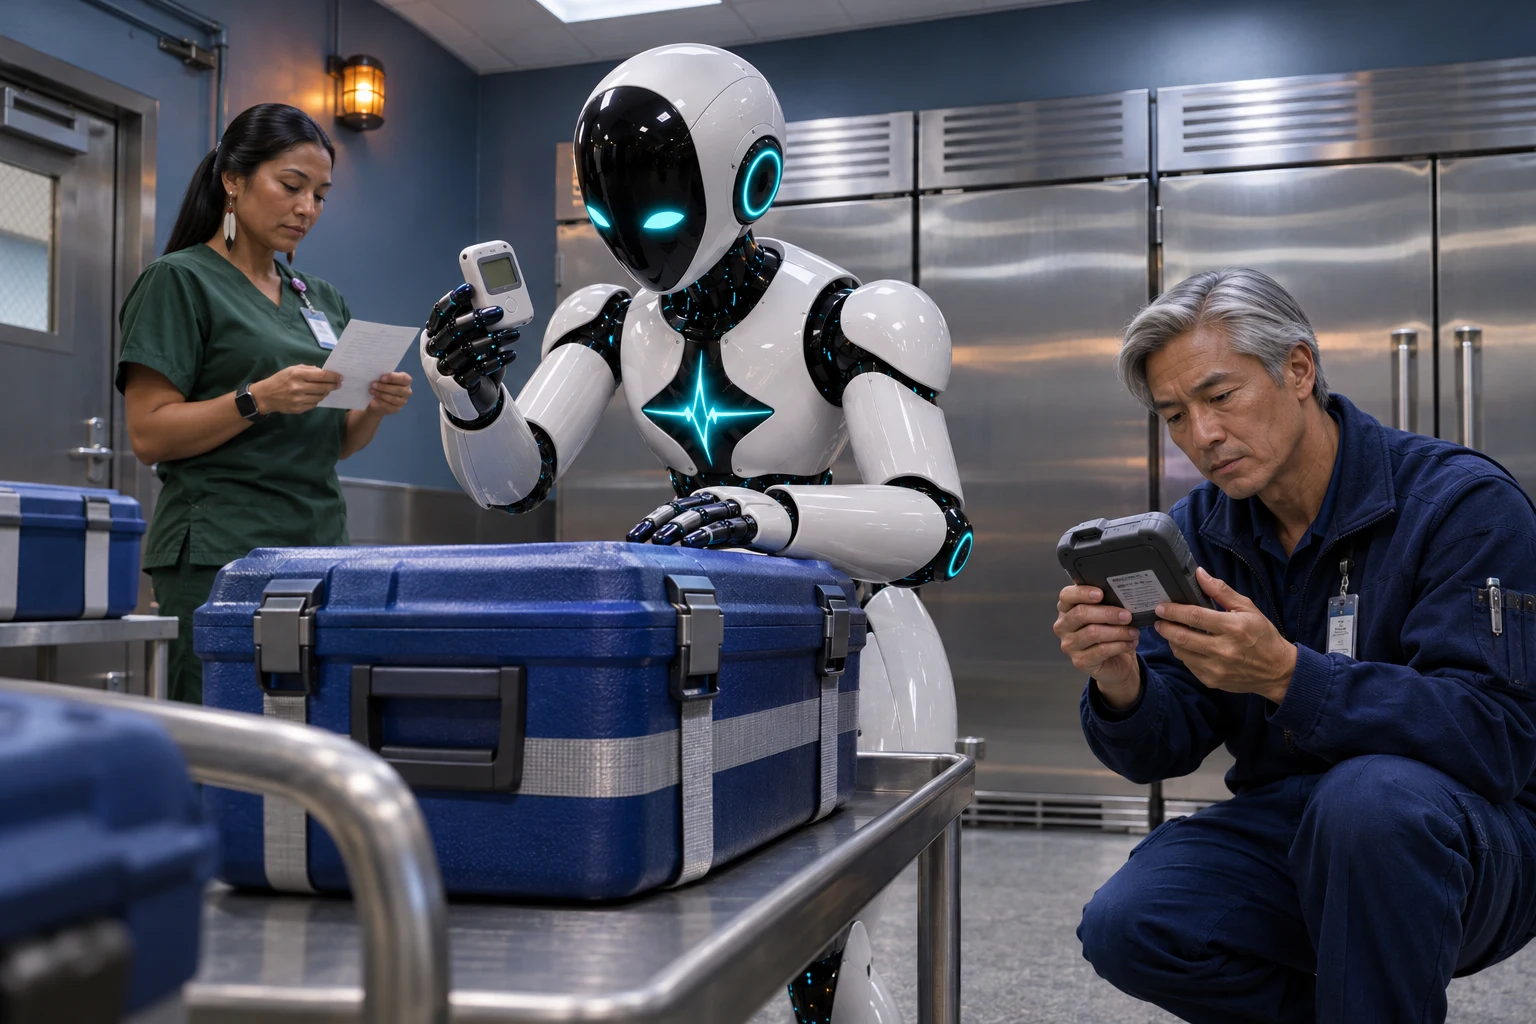
Reported: A November 5, 2026 joint CISA, FBI, HHS, USDA and DOT fact sheet warns of cyber activity targeting refrigeration controls and cold-chain monitoring. Attackers can alter temperatures or hide temperature readings. The agencies recommend removing public internet exposure, securing necessary remote access, changing default passwords and updating firmware.
DomAfina’s take: for home-care teams relying on refrigerated medicines or supplies, the risk extends beyond the EMR. Ask suppliers who receives temperature alarms, how readings are independently checked and what happens if monitoring goes offline. Document an escalation contact and a backup supply plan. Route any storage concern to the responsible pharmacist or supplier before use. This is a supply-chain readiness check—not evidence that a home-care provider has been attacked.
Source reviewed: Joint federal cold-chain fact sheet, November 5, 2026. The source supports the reported update; the operational recommendations are DomAfina’s analysis.
Discussion
Comments and replies
Keep it useful and on this article’s subject. No profanity, hate, threats, harassment, spam, advertising, solicitation, personal or patient information. Off-topic comments are held for moderation and automatically deleted after 10 days if not approved.
Loading recent comments…